A community member inquired about the official support for Boolean columns in ControlUp when written to via a PowerShell script. They noted that their script was functioning as expected, showing a dropdown with options for "true" and "false" instead of a plain text box for the Boolean field. This behavior indicates that Boolean fields are recognized and handled appropriately within the ControlUp system's indexing and UI.
The confirmation came from multiple users, including a ControlUp expert, that Boolean fields are indeed supported. ControlUp's platform supports defining columns with Boolean data types, enabling users to interact with these fields through dropdown selectors for true/false values, which enhances data consistency and ease of use.
This means that scripts or automation workflows that write Boolean values into ControlUp indexes can rely on native support for true/false states. This feature is useful for scenarios where binary states need to be tracked and toggled directly from the ControlUp interface without requiring manual text input.
For more detailed information on supported data types and scripting integration with ControlUp indexes, users can refer to the official ControlUp documentation at https://docs.controlup.com, and consider the ControlUp Academy (https://cuacademy.controlup.com) for deeper learning resources on scripting and data management in ControlUp.
Read the entire article here...
ControlUp Scripts & Triggers Training & Support Archives
ControlUp Script and Trigger training and support-related archives from inside the ControlUp Community on Slack.
How to Identify and Manage Duplicate Devices in ControlUp Desktops Due to Reimaging and Agent Re-registration
A common challenge with ControlUp's Desktops product arises when IT teams test new device models by repeatedly reimaging machines, causing multiple instances of the same device to register with unique device IDs but identical hostnames. This scenario leads to an inflated license count, as each registration consumes a license until the devices are flagged inactive and subsequently removed from the system.
To identify these "duplicate" devices, one effective method involves querying the ControlUp `device_status` data index. While leveraging ControlUp Dashboards can help visualize this data, caution is advised when running queries based solely on device IDs without applying appropriate filters to avoid misleading results. Advanced options in the dashboard allow adding additional metrics that can pinpoint such duplicates by hostname or device name, which is particularly helpful since the root issue is not duplicate device IDs but duplicate device names retained after reimaging.
In practice, customizing dashboard widgets with additional filters and metrics can enable teams to monitor and isolate devices that have been repeatedly reimaged and registered, streamlining license management. For devices already deployed, it is possible to run a script that forces re-registration of devices with a new unique ID to prevent license count inflation. This step may be beneficial where device IDs need to be refreshed or reset in the ControlUp environment.
Another important factor involves deployment parameters. For example, the `REGISTERWITHNAME=1` flag, if set during agent deployment, can cause devices to register under the same name, exacerbating duplicate name issues. However, in many cases, the default setting with the `ALLUSERS=1` flag, used in ControlUp's standard installer from the Downloads pane, is sufficient and does not trigger duplicate registrations unless devices are repeatedly reimaged and reset by users.
Overall, the underlying cause of the inflated license usage is the repeated device reimaging and agent re-registration under the same hostname but with unique IDs. Proper use of the `device_status` index for querying, cautious dashboard configurations, potential scripting to reset device IDs, and awareness of deployment flags can effectively manage and mitigate "duplicate" device issues within the ControlUp Desktops product.
Read the entire article here...
Read the entire article here...
How to Configure AND vs OR Logic with Device Tags in ControlUp Alerts
When configuring alerts in ControlUp based on device tags, a frequent question arises regarding whether selecting multiple device tags in the alert conditions operates as an OR or AND logic. It was clarified that in the current ControlUp alert configuration interface, when multiple device tags are selected, the alert triggers if the device has any one of the specified tags. This means the condition acts as a logical OR between the tags rather than an AND.
The user interface presents these tag selections as checkboxes, limiting the direct ability to express compound AND logic (such as requiring both tags to be present simultaneously). There is no built-in switch or toggle to explicitly select AND versus OR behavior for device tag conditions. While the idea of combining tags using expressions like "tag1&&tag2" was discussed, this is not supported directly within the tag selection box, and typing such expressions does not function as a filter in the UI.
However, a workaround approach involves leveraging multiple alert conditions, which are inherently ANDed together by ControlUp. For instance, instead of trying to combine two tags in one condition, you can create two separate conditions that must both be true, effectively achieving an AND between device tag criteria. Since tags are treated as string fields in the system, operators such as "contains" or "=" can be used in these conditions. Using "contains" is useful but may lead to partial matches, which requires careful tag naming conventions to avoid unintended matches (e.g., "reboot_device" matching both "reboot_device" and "no_reboot_device").
To address this, users have adapted by modifying their tagging strategies to use more distinctive and unambiguous tag names like "device_reboot_yes" and "device_reboot_no," which helps ensure that the use of "contains" or equality checks does not overlap between conflicting tags. Some users also explored adding exclusion conditions (e.g., conditions that exclude devices with certain tags), but these might not cover all scenarios adequately.
The community suggested it would be valuable for ControlUp to enhance alert configuration with explicit AND/OR toggles or support for string operations like "starts with" to improve flexibility for tag-based alerting. Meanwhile, using multiple conditions combined with clear tag naming conventions is the recommended practical approach for achieving AND logic with device tags in alerts.
For more detailed information on alert condition configuration and tag-based filtering, refer to the official ControlUp documentation at https://docs.controlup.com. This includes guidance on condition operators, tag management, and best practices for alert configurations.
Read the entire article here...
Read the entire article here...
Automating Detection and Remediation of Stuck BitLocker Encryption on Windows 11 Endpoints with ControlUp Real-Time Automation Engine
When deploying hundreds of Windows 11 endpoints managed by Intune, a common issue with BitLocker encryption is that the process sometimes becomes stuck at a certain percentage completion. While manually pausing and restarting the encryption process resolves the issue within minutes, automating this detection and remediation can save considerable time and ensure consistent endpoint security.
Using ControlUp Real-Time Automation Engine (CU4D), such automation is achievable by leveraging scripted detection and remediation. One approach is to create a single script that both detects the encryption status and initiates a restart of the encryption process if it remains stuck at the same percentage. This script can be deployed across all affected devices and scheduled to run periodically, for example, once per day, to identify any stuck BitLocker jobs and resolve them promptly.
A more modular approach involves creating two separate scripts: a detection script and a remediation script. The detection script would check the current encryption percentage, and if it identifies a stuck state, it writes the status to a custom index attribute within ControlUp. An alert can then be configured based on the value of this custom attribute. When the alert triggers due to a stuck encryption status, the remediation script executes automatically to restart the BitLocker encryption, ensuring a timely resolution without manual intervention.
This method harnesses ControlUp's ability to store custom scripted outputs in custom indices and link those to alert triggers, thus providing a robust, automated way to handle encryption stalls on Intune-managed Windows 11 devices. For further details on configuring custom scripts, custom indices, and alerts in ControlUp, administrators can refer to ControlUp's documentation at https://docs.controlup.com and explore automation capabilities in the ControlUp Academy at https://cuacademy.controlup.com.
Read the entire article here...
Read the entire article here...
How to Report Horizon Client Versions Across User Sessions Using ControlUp
A common requirement for managing VMware Horizon environments is the ability to report on the endpoint client versions—referred to as "HZ Client Version"—used by users to connect to the Horizon infrastructure. This need becomes particularly important in hybrid environments where users connect from both managed internal devices and unmanaged BYOD (Bring Your Own Device) endpoints. Tracking client versions helps administrators identify devices running outdated Horizon clients that require upgrades to ensure security, compatibility, and optimal performance.
Within ControlUp, the Horizon client version information can be accessed via several mechanisms. The VDI - Details view in the ControlUp console displays the HZ Client Version associated with each session, providing a straightforward way to see the current client version used. For programmatic or historical data extraction needs, ControlUp also offers a real-time data API (https://api.controlup.io/reference/gettables) which can retrieve live session details including client versions. Additionally, the "initial HZ client version" field recorded in the Session Activity report captures the client version that was used to start the session. This field, although labeled as "initial," effectively serves as a snapshot of the client version at session start.
However, because users in hybrid scenarios may connect multiple times throughout the week from different devices or update their Horizon client between sessions (for example, by disconnecting, updating, and reconnecting), it is important to consider that the client version can vary across sessions. The "initial HZ client version" is tied to each individual session start, so accumulating this information over a period allows administrators to identify all versions in use and target users on outdated clients. Pulling session activity reports over time and correlating the client versions used enables identification of BYOD devices needing updates even if the same user connects from multiple endpoints.
In summary, the "initial HZ client version" contained in ControlUp’s Session Activity reports is the key field for tracking Horizon client versions across user sessions. The ControlUp real-time data API further facilitates custom querying and automation for this reporting. For detailed exploration of session data, the VDI - Details view complements these options with an at-a-glance interface. Using these tools, administrators in hybrid environments are able to efficiently monitor and manage Horizon client versions on both managed and BYOD devices, ensuring compliance and performance consistency.
Read the entire article here...
Read the entire article here...
ControlUp Community Meetup 16: From DEX to Autonomous IT: A Fireside Chat with ControlUp CEO Jed Ayres
In this ControlUp Community Meetup, host Douglas Brown sits down with Jed Ayres, CEO of ControlUp, to discuss the growing complexity of IT, the evolution of Digital Employee Experience, and how AI is changing the way technology teams identify and resolve problems.
Read the entire article here...
Read the entire article here...
Managing Disk Usage on Laptops with ControlUp SIP Agent
ControlUp provides a scripting engine within ControlUp for Desktops, enabling IT administrators to distribute and execute scripts across devices in their environment. This functionality allows for tasks such as IT administration and data collection. ([support.controlup.com](https://support.controlup.com/docs/scripting-guide?utm_source=openai))
To utilize this feature, navigate to ControlUp for Desktops > Configuration > Scripts to view and manage your scripts. The Scripting Guide offers comprehensive instructions on running scripts in ControlUp for Desktops. ([support.controlup.com](https://support.controlup.com/docs/scripting-guide?utm_source=openai))
For managing disk usage on laptops equipped with the SIP agent, you can adapt existing scripts designed for VDI environments. The Scripting Guide provides detailed information on creating and managing scripts, which can be tailored for laptops. ([support.controlup.com](https://support.controlup.com/docs/scripting-guide?utm_source=openai))
Additionally, the ControlUp Script Library offers a collection of useful scripts compiled by ControlUp, which can be imported and customized for your specific needs. ([controlup.com](https://www.controlup.com/scripts/?utm_source=openai))
By leveraging these resources, you can effectively monitor and manage disk usage on laptops using the SIP agent, similar to the capabilities available for VDIs.
Read the entire article here...
Read the entire article here...
How to Deploy ControlUp Agent via GPO in VDI Environments with MSI Silent Install and PowerShell Automation
Deploying the ControlUp Agent for VDI environments via Group Policy Object (GPO) does not have a dedicated official knowledge-base article, as the installation approach aligns with generic MSI silent installs used in other deployment methods like SCCM or PDQ. The official ControlUp documentation regarding local machine connection and agent communication is the primary reference for deployment: https://support.controlup.com/docs/connect-to-your-machines-locally and https://support.controlup.com/docs/agent-outbound-communication.
For non-persistent VDI setups that use a gold master image, the recommended method is to install the ControlUp agent MSI directly on the master image with specific MSI properties: `MASTER_IMAGE=true`, along with the `AUTHKEY` and `RegistrationKey`. This avoids the need for repeated installations on cloned machines via GPO. For persistent, domain-joined virtual machines, using a GPO Computer Startup Script to run an msiexec command is preferred over GPO Software Installation because it allows passing required MSI properties. An example command line looks like this:
`msiexec /i \\share\ControlUpAgent-xxxx.msi /qn AUTHKEY="" RegistrationKey="" MASTER_IMAGE=true`
The authentication keys are retrieved from the Real-Time Console under Settings → Agent. The Registration Key is mandatory starting from version 9.0. Machines must be manually added to the organization tree unless the agent version is 9.0.5 or higher, which supports self-registration.
When GPO deployment is not optimal, if remote RPC or WMI connectivity is available, deploying the agent remotely via the ControlUp console or Monitor is simpler. For cloud-managed endpoints, Microsoft Intune is the officially documented deployment method.
A practical example was shared demonstrating a PowerShell script to deploy the ControlUp Agent MSI for VDI within a Nerdio scripted action context. The script copies the MSI from a UNC file share to a local temporary path, validates that the MSI file is correctly copied (including a check on the MSI magic bytes), and then executes the msiexec command with silent installation flags, the authentication keys, and logging enabled. It captures and reports installation exit codes and prompts when a reboot is required. The script also includes a post-installation check to list ControlUp-related services to confirm the agent installed and started as expected.
This approach encapsulates the best practice for deploying ControlUp agents in VDI environments using GPO, balancing MSI property requirements, version-specific authentication mechanisms, and practical scripting for automation. For detailed agent deployment contexts and command-line references, the ControlUp official documentation remains the authoritative source: https://support.controlup.com/docs/connect-to-your-machines-locally and https://support.controlup.com/docs/agent-outbound-communication.
Read the entire article here...
Read the entire article here...
How to Configure Low Disk Space Alerts by Percentage in ControlUp for Devices
In ControlUp for Devices (CU4D), setting up an alert to notify an administrator when any device's OS disk free space drops below a certain threshold can be configured through the Events > Alert Rules section. To create an alert for low disk space, a user needs to define the appropriate category, metric, condition, and value that represent the target threshold.
The recommended approach is to use an alert rule that monitors the free space on the OS disk. While the initial example provided in the community discussion suggested a value-based threshold (e.g., a specific number of gigabytes free), it is also possible to configure an alert based on a percentage of free disk space. This is important for flexibility as percentages provide a more relative and scalable measure across devices with different disk sizes.
To implement this, the alert should be defined in the category related to storage or disk metrics. The metric to monitor would be the percentage of free space available on the OS disk. The condition would then be set to trigger when this percentage falls below a certain value (such as 10%). Once the alert triggers, it can be configured to send an email notification to administrators. Furthermore, ControlUp’s integration with script actions can automate responses to these alerts, such as running a system disk cleanup or presenting a user prompt to clean up space.
For detailed steps and additional options, users are encouraged to refer to the official ControlUp documentation on alert rules and script actions, as well as the ControlUp Knowledge Base and Academy resources at https://docs.controlup.com and https://cuacademy.controlup.com. These resources provide comprehensive guidance on setting conditions, selecting metrics, and automating remediation workflows based on alerts.
Read the entire article here...
Read the entire article here...
NEW ControlUp Disk cleanup script that actually asks the user what to delete
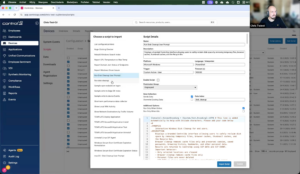
Chris Twiest demos a new interactive disk cleanup utility built by Sebastien Perusat and now baked into the product. Instead of silently cleaning from the system context, it prompts the end user with what can be reclaimed and lets them choose — recycle bin, temp files, browser cache. Works on Windows and macOS, can be triggered manually or from an alert, writes results to a data index and a device event, and is fully editable. Available in the script library now.
Read the entire article here...
Read the entire article here...